# Blocking vs Detection Mode in Zen Firewall
Zen Firewall by Aikido offers two operational modes for handling attack patterns: **Detection Mode** and **Blocking Mode**. These modes specifically apply to application-level attacks like SQL injection, shell injection, path traversal, and SSRF.
Other security features like [user blocking](https://help.aikidogov.us/zen-firewall/zen-features/blocking-users-with-zen-firewall), [bot protection](https://help.aikidogov.us/zen-firewall/zen-features/blocking-bot-traffic-with-zen-firewall), [tor blocking](https://help.aikidogov.us/zen-firewall/zen-features/blocking-tor-traffic-with-zen-firewall) and [country blocking](https://help.aikidogov.us/zen-firewall/zen-features/blocking-traffic-by-country-with-zen-firewall) are managed separately through their respective settings.
## Understanding the Modes
### Detection Mode (Default)
* 📝 Logs potential attacks without blocking them
* 🔬 Allows you to monitor threats without impacting traffic
* 📊 Helps evaluate security patterns before enabling blocks
### Blocking Mode
* 🛡️ Actively blocks detected attack patterns
* 🚫 Blocks malicious requests before they can execute
* ⚡ Provides real-time protection against threats
## Configuration Options
### Using Environment Variables
```
# Enable Blocking Mode
AIKIDO_BLOCK="true"
# Enable Detection Mode (default)
AIKIDO_BLOCK="false"
```
### Using the Dashboard
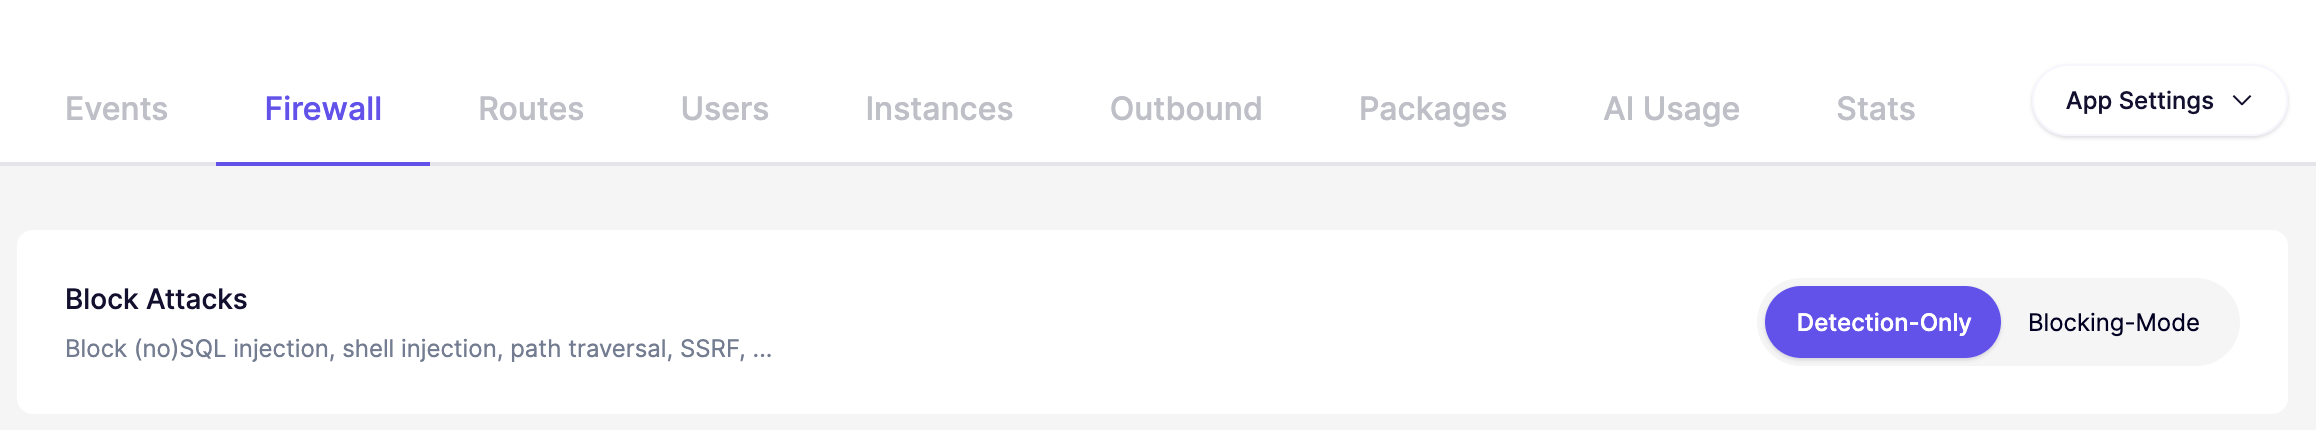
1. Navigate to your app's firewall settings
2. Find the "**Block Attacks**" section
3. Toggle between "Detection-Only" and "Blocking-Mode"
{% hint style="info" %}
Note: The environment variable sets the initial mode, but the dashboard configuration takes precedence once loaded.
{% endhint %}
## What Gets Blocked?
Blocking mode only affects these attack types:
* SQL Injection attempts
* NoSQL Injection attempts
* Shell Injection attacks
* Path Traversal exploits
* SSRF attempts