
Malware Monitor Report
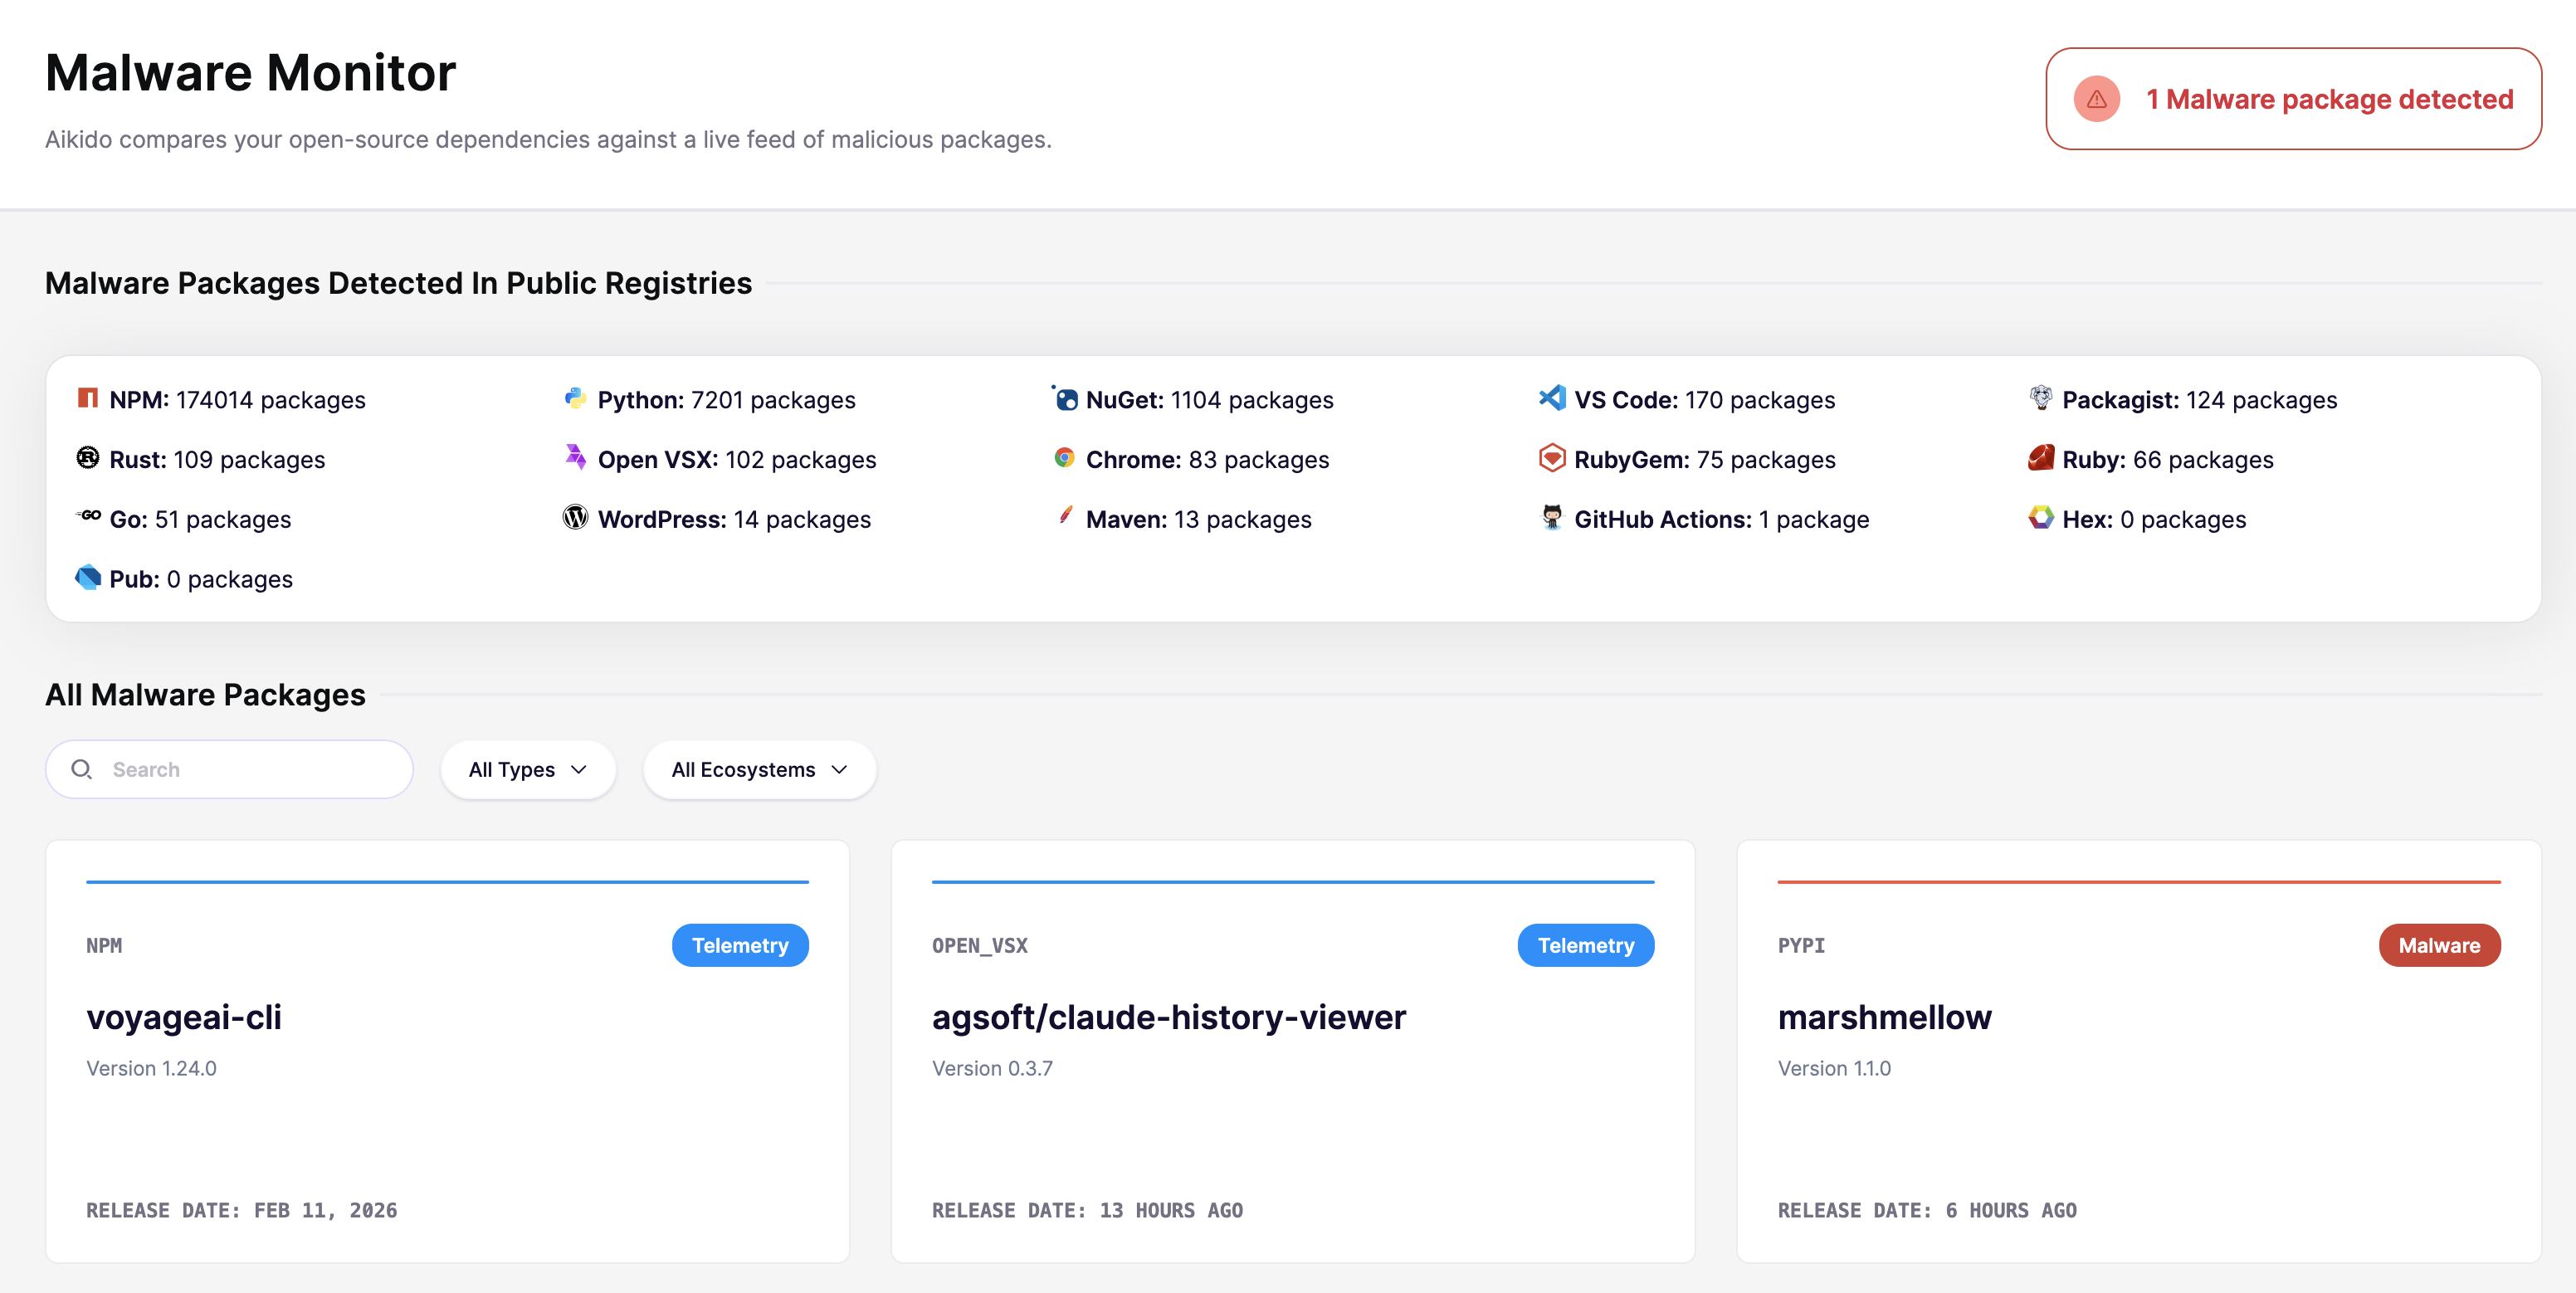
The Malware Monitor gives you visibility into malicious packages published in public registries and shows whether they affect your environment.
Aikido continuously compares your dependencies against a live feed of known malicious packages across ecosystems such as npm, PyPI, NuGet, Maven, RubyGems, VS Code extensions, and more.
If a malicious package is detected in your projects, you are alerted immediately. Use Safe-Chain to block Malware from getting installed on your machines.
When to use this report
Use the Malware Monitor when you need to:
- Detect malicious open source packages before they cause damage
- Respond to supply chain incidents
- Demonstrate protection against dependency based attacks
- Monitor newly published threats in public registries
- Reassure customers about third party risk
This report focuses specifically on intentional malware, not regular vulnerabilities.