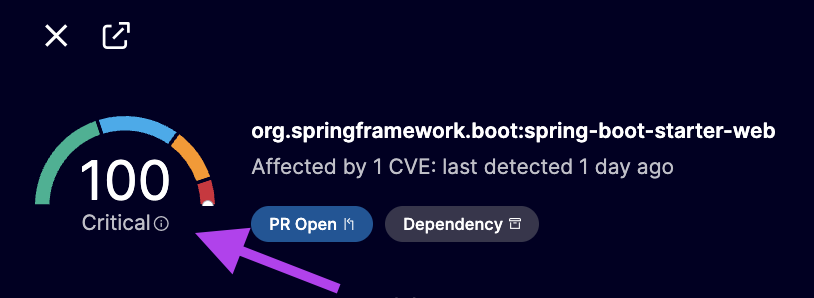
How is Severity Score Calculated
Aikido provides a contextual, risk-based severity score from 0 to 100, offering 10× more granularity than traditional CVSS scoring (which is on a 0–10 scale). This allows for better prioritization and filtering.
| Severity | Score |
|---|---|
| Critical | 90 - 100 |
| High | 70 - 89 |
| Medium | 40 - 69 |
| Low | 1 - 39 |
1. Multiple Vulnerability Data Sources
We continuously monitor a variety of vulnerability feeds and databases, that provide baseline severity information and help establish initial severity scores. Databases include:
- Public vulnerability databases (e.g., NVD, GHSA,... | See full list)
- Operating system and vendor-specific advisories
- Our own Aikido Intel: https://intel.aikido.dev/
2. Contextual Severity Adjustments
To reflect actual risk more accurately, Aikido layers in additional context such as exploitability, environment, threat intelligence, and custom rules.
Exploitability & Threat Intelligence:
Severity can increase when there’s evidence of real-world risk:
- The vulnerability is actively exploited or appears on the CISA KEV list
- A public PoC exploit is available (e.g., on GitHub)
Business Context
Severity is adjusted based on the importance of the affected asset. Some example are:
- Production vs test environments
- Backend vs frontend code
- Whether the vulnerable code is reachable or executed
Customer Rules
You can further refine issue scoring by adding contextual information to your project
- Learn how you can improve the risk score for repositories and containers here
Exploit Prediction (EPSS)
Aikido also supports EPSS-based prioritization to automatically downgrade or ignore vulnerabilities that are unlikely to be exploited in the next 30 days. This is optional and turned off by default, more info here: use-epss-values-to-further-reduce-noise.md
You can click the score to view a detailed breakdown of why this issue received this severity rating