
Blocking vs Detection Mode in Zen Firewall
Zen Firewall by Aikido offers two operational modes for handling attack patterns: Detection Mode and Blocking Mode. These modes specifically apply to application-level attacks like SQL injection, shell injection, path traversal, and SSRF.
Other security features like user blocking, bot protection, tor blocking and country blocking are managed separately through their respective settings.
Understanding the Modes
Detection Mode (Default)
- 📝 Logs potential attacks without blocking them
- 🔬 Allows you to monitor threats without impacting traffic
- 📊 Helps evaluate security patterns before enabling blocks
Blocking Mode
- 🛡️ Actively blocks detected attack patterns
- 🚫 Blocks malicious requests before they can execute
- ⚡ Provides real-time protection against threats
Configuration Options
Using Environment Variables
# Enable Blocking Mode
AIKIDO_BLOCK="true"

# Enable Detection Mode (default)
AIKIDO_BLOCK="false"
Using the Dashboard
- Navigate to your app's firewall settings
- Find the "Block Attacks" section
- Toggle between "Detection-Only" and "Blocking-Mode"
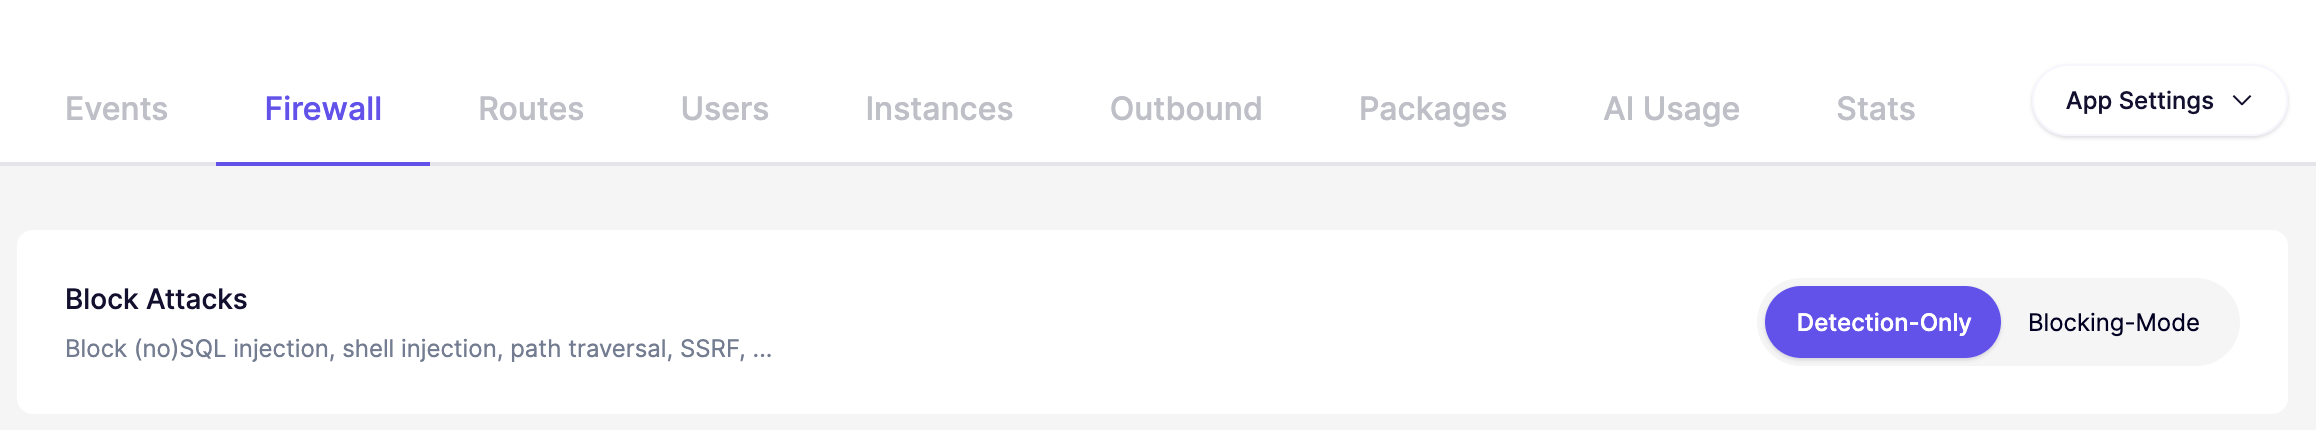
Note: The environment variable sets the initial mode, but the dashboard configuration takes precedence once loaded.
What Gets Blocked?
Blocking mode only affects these attack types:
- SQL Injection attempts
- NoSQL Injection attempts
- Shell Injection attacks
- Path Traversal exploits
- SSRF attempts