
PHP on Fly.io
This guide will walk you through installing and setting up Zen Firewall by Aikido for your application. Follow the steps below to protect your application.
If you encounter any issues or problems, don't hesitate reach out on support chat or Github issues
https://github.com/AikidoSec/firewall-php
Requirements
- PHP 7.2+ (tested up to PHP 8.5).
- Fly.io PHP deployment runtime.
- Aikido account & Zen Firewall token
Installation & Configuration
Install Zen Firewall by Aikido
Set Fly secrets:
fly secrets set AIKIDO_TOKEN=AIK_RUNTIME_...
fly secrets set AIKIDO_BLOCK=false
Create
.fly/scripts/aikido.sh:#!/usr/bin/env bash cd /tmp curl -L -O https://github.com/AikidoSec/firewall-php/releases/latest/download/aikido-php-firewall.x86_64.deb dpkg -i -E ./aikido-php-firewall.x86_64.debDeploy:
fly deployVerify installation
Check module status:
fly ssh console
php -i | grep "aikido support"
Expected output includes
aikido support => enabled.Enable Request Blocking and User Identification
Use this middleware to enable rate limiting, user identification, and blocking features.
Zen Firewall does not require this middleware to block attacks. Core attack protection works without it. The middleware provides additional request context that Zen uses for protections such as rate limiting, user blocking, bot blocking, country blocking, and threat actor blocking.
Adapt the example to fit how your application identifies users and handles requests.
Use
set_userandshould_block_requestin your request pipeline:if (extension_loaded('aikido')) { \aikido\set_user('123', 'John Doe'); $decision = \aikido\should_block_request(); if ($decision->block) { if ($decision->type === 'ratelimited') { http_response_code(429); header('Retry-After: ' . $decision->retry_after); exit('You are rate limited by Zen.'); } http_response_code(403); exit('You are blocked by Zen.'); } }Test your app
Browse to your application and perform a couple of actions or open a couple of pages. Zen will automatically discover the routes in your application.
Zen sends data back to Aikido every 10 minutes
You can verify a working agent by looking at the following pages of your Zen application:
- Events: Should show an "Application started" event.
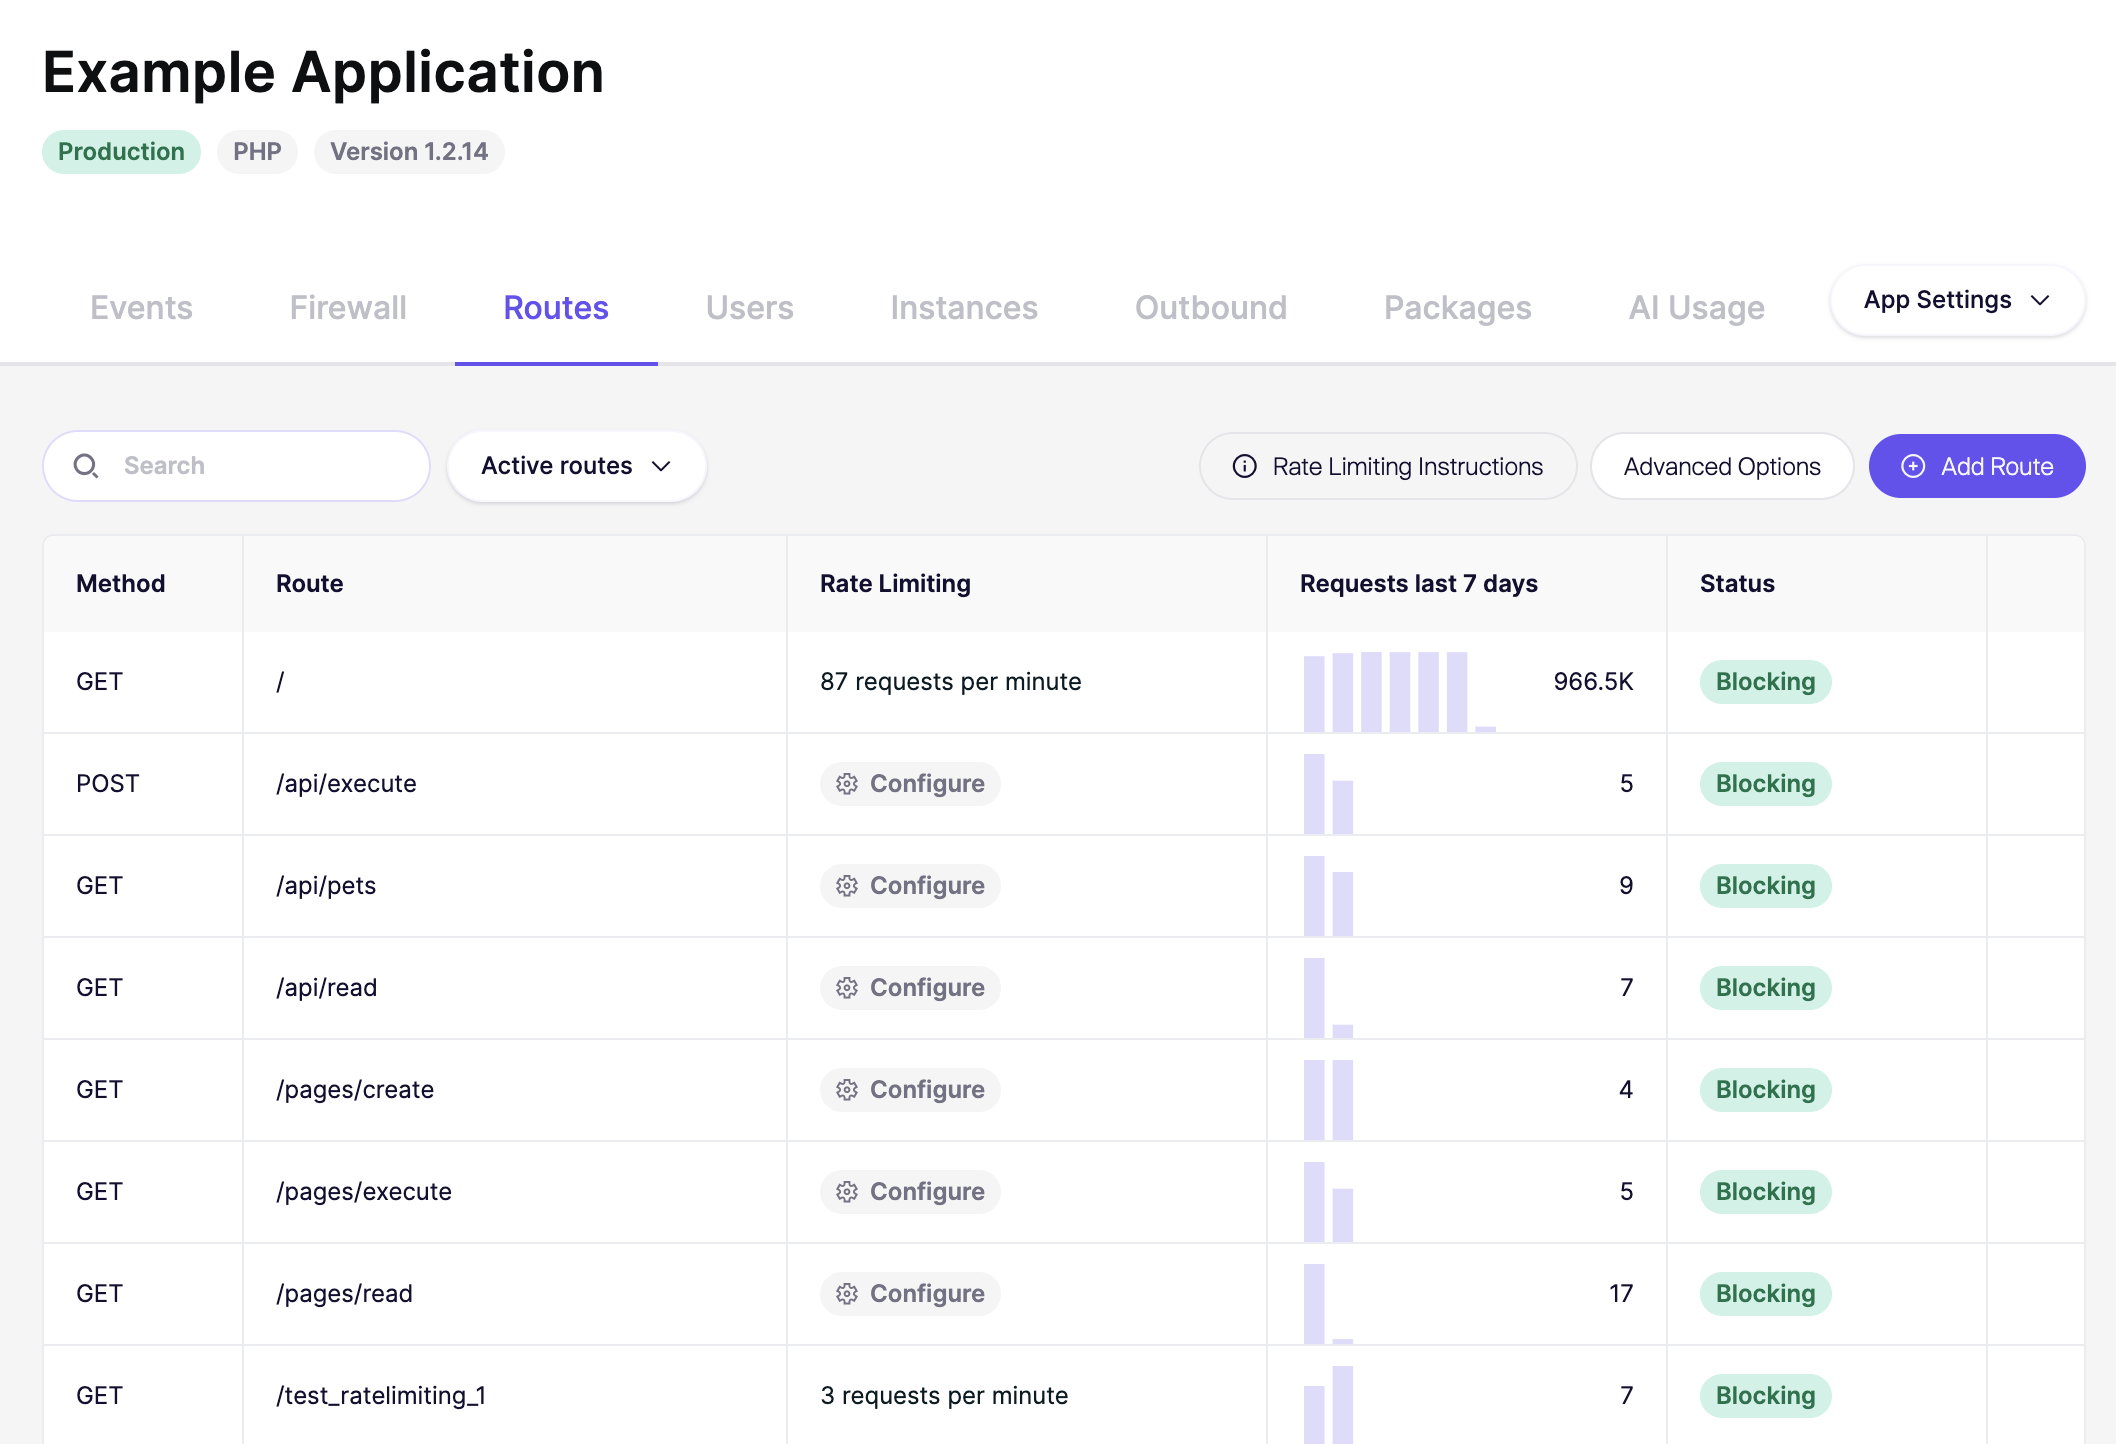
- Routes: After some time your application routes will start showing here with the method, route and requests.
- Instances: Should show the number of active instances for your application where Zen is installed.
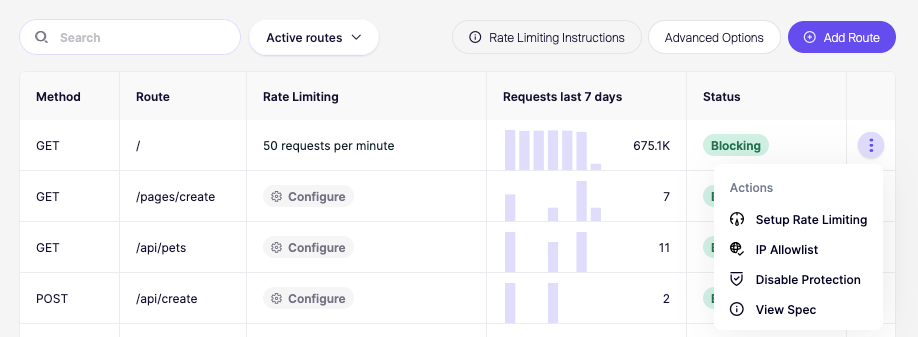
Setup rate limiting in the dashboard
When you've added the Zen Firewall middleware you can test protecting a route from brute force attacks, you do this by setting up rate limit in the Aikido Dashboard:
- Click on the created app.
- Go to the Routes tab.
- Find the route you would like to limit and click Setup rate limiting.
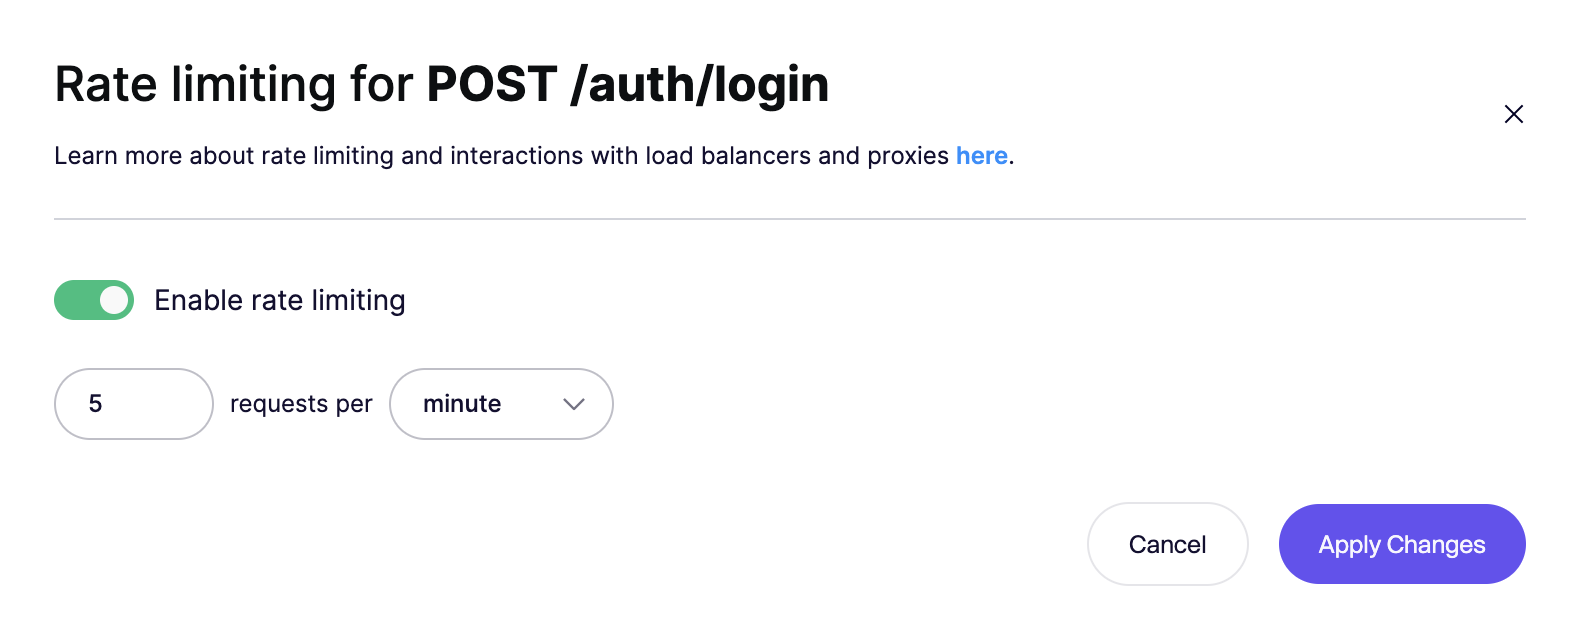
- Follow the instructions to configure the rate limit (e.g., 5 requests per minute).
Verify Rate Limiting
Start your app and try to access the route you've rate limited 5 times within a minute. After the fifth attempt, you should receive a rate limit error:
You are rate limited by Aikido firewall. (Your IP: 1.2.3.4)Next steps
Congrats you've successfully installed Zen Firewall. If you encountered any problems, have concerns or feature requests, don't hesitate to reach out to support.
You can now go and explore the many features that Zen Firewall provides:
- blocking-bot-traffic-with-zen-firewall.md
- blocking-tor-traffic-with-zen-firewall.md
- blocking-users-with-zen-firewall.md
- blocking-known-threat-actors-with-zen-firewall.md
- blocking-traffic-by-country-with-zen-firewall.md
- setting-up-rate-limiting-for-routes.md
- monitor-outbound-domains.md
Additional information: